Tech Leaders and Governments Divided Over AI Safety Risks
Technology leaders and governments are increasingly divided over how to manage the risks of advanced artificial intelligence. While Anthropic, OpenAI and several other industry figures support stronger safeguards and coordinated action, Meta and Nvidia have questioned the need for a regulated slowdown. Recent discussions in the United Kingdom and international calls for AI oversight have brought the debate into sharper focus: how can the world benefit from faster AI development without losing control of its risks?
Tech Leaders and Governments Divided Over AI Safety Risks
The debate over artificial intelligence is moving beyond what AI can accomplish to a more difficult question: how far should its development go before stronger safeguards become mandatory?
Technology executives, researchers and government officials increasingly agree that powerful AI systems need careful oversight. However, they disagree on the urgency of the risks, the role governments should play and whether companies should slow development to give safety measures time to catch up.
The disagreement became particularly visible in September 2026, when prominent technology figures debated proposals for coordinated action on advanced AI. Developments in October, including a UK parliamentary hearing and new funding for AI safety research, have kept the issue in the spotlight.
At the heart of the argument is a difficult balance. Restricting AI too aggressively could limit innovation and economic opportunities. Moving too quickly, however, could leave governments and businesses struggling to manage risks that are difficult to predict.
Why AI Safety Has Become a Major Debate
Artificial intelligence has advanced from systems that generate text and images to increasingly capable tools that can write software, analyze information and perform multistep tasks. More autonomous systems can potentially interact with digital services and carry out actions with less direct human involvement.
These capabilities offer practical benefits. Businesses can automate routine work, researchers can investigate complex problems, and developers can build applications more quickly. But greater capability can also introduce new security and reliability challenges, particularly when an AI system can access sensitive information or take consequential actions.
Some researchers and technology executives are concerned about risks that extend beyond individual mistakes. These include AI-assisted cyberattacks, the misuse of powerful models, unreliable autonomous decisions and, in more extreme scenarios, the possibility that future systems could become difficult for humans to control.
Not everyone agrees that the most severe scenarios are likely or imminent. Critics of the so-called AI doom debate argue that speculative predictions should not distract policymakers from measurable problems such as fraud, privacy violations, biased decisions, job disruption and the misuse of existing AI tools.
The disagreement is therefore not simply between people who support AI and those who oppose it. Many participants support continued development but differ over which risks deserve priority and what safeguards should be required.
Anthropic and OpenAI Support Stronger Safeguards
Anthropic CEO Dario Amodei has argued for a more coordinated approach to the development of increasingly capable AI systems. In September, he called for the industry to consider how quickly frontier models should advance and how safety measures could keep pace.
OpenAI CEO Sam Altman has also expressed support for careful development and stronger coordination around advanced AI risks. Other prominent figures, including Elon Musk and Google DeepMind's Demis Hassabis, have supported efforts to improve AI safety, although their specific positions and preferred approaches are not identical.
Supporters of stronger safeguards argue that companies cannot rely exclusively on voluntary promises when developing systems that could affect millions of people or critical infrastructure. They want more systematic evaluations, better information sharing and closer cooperation between AI developers and governments.
The argument becomes especially important when AI systems are capable of assisting with complex technical tasks. A model that performs well during ordinary testing might behave differently in an unfamiliar environment, when given unusual instructions or when connected to external tools. Independent testing can help identify such weaknesses before a system is widely deployed.
However, calls for a slowdown do not necessarily mean stopping all AI research. Proposals vary, ranging from additional testing and controlled access to more formal agreements about the development and release of the most capable models.
Meta and Nvidia Question the Need for a Regulated Slowdown
Other technology leaders are less convinced that new restrictions or a coordinated slowdown are the right response.
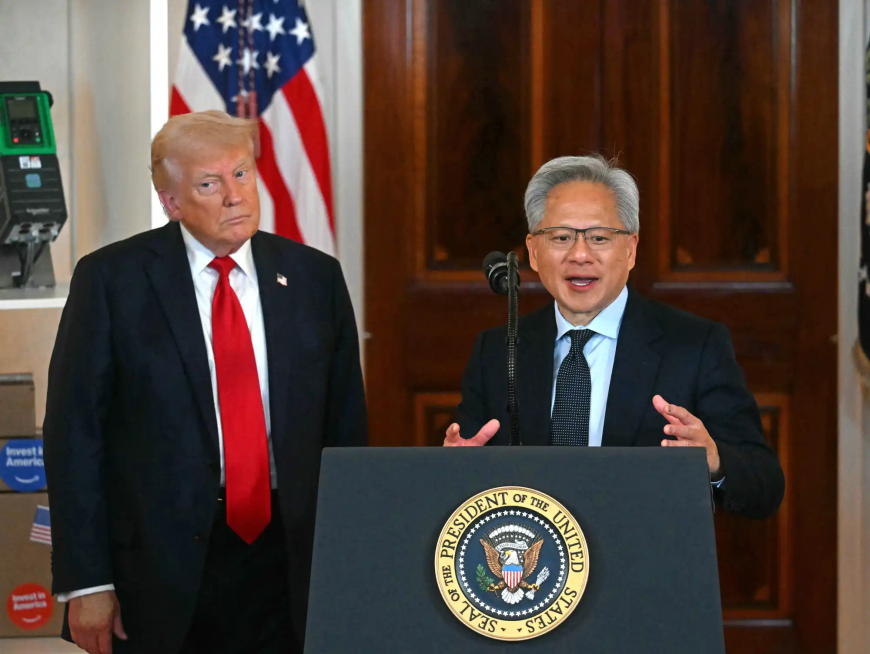
Meta CEO Mark Zuckerberg has emphasized market-led approaches and the role of companies in developing safeguards. Nvidia CEO Jensen Huang has also questioned the need for additional regulation, reflecting concerns that restrictive rules could interfere with innovation.
These positions matter because AI development depends on a complex commercial ecosystem. Companies invest heavily in computing infrastructure, semiconductor technology, research teams and data centres. Delays or new compliance requirements can affect product schedules, operating costs and competition.
Supporters of a lighter regulatory approach argue that companies should retain room to experiment, improve safety through technical progress and respond to emerging problems without waiting for legislation. They also warn that rules designed around today's systems could become outdated as technology changes.
The opposing concern is that commercial competition can create incentives to release increasingly capable products quickly. If companies are rewarded for being first to market, voluntary safety commitments may not always be enough to prevent risky decisions.
There is also a practical disagreement over who should decide when a model is safe enough to release. Developers understand their systems better than most outside observers, but independent regulators may be better positioned to examine public risks without being directly responsible for a product's commercial success.
The United Kingdom's AI Regulation Debate Intensifies
The United Kingdom has become an important centre of discussion about how governments should oversee advanced AI.
On October 13, 2026, representatives from OpenAI and Anthropic supported legally binding AI safety rules during a UK parliamentary hearing, according to reporting by WIRED. Representatives from Google DeepMind and Meta did not endorse the same approach, favouring standards and existing regulatory structures instead.
The hearing highlighted a central weakness in voluntary oversight: government bodies may have limited authority to compel cooperation from AI developers. The UK's AI Security Institute, which evaluates risks from advanced AI systems, has faced questions about the limits of its inspection powers.
Participants also raised concerns about the speed of development and whether existing safeguards are sufficient to address emerging risks. The discussion included evidence from former industry employees and whistleblowers who questioned whether companies could reliably regulate themselves.
The disagreement does not mean that all AI companies oppose regulation or that every government official supports strict controls. Rather, it illustrates how difficult it is to agree on enforceable requirements while the technology continues to evolve.
For policymakers, the challenge is to establish rules that are strong enough to address serious risks without making compliance unnecessarily difficult for smaller developers and researchers.
Nvidia Pledges $250 Million for UK AI Safety Research
On October 14, Nvidia announced a commitment of $250 million worth of computing resources over five years to support AI safety research in the United Kingdom, Reuters reported.
The commitment represents $50 million annually and is intended to support work on the evaluation and safety of agentic AI systems. These systems can perform sequences of tasks and interact with tools or digital environments rather than simply generating a response to a single prompt.
The initiative is expected to support research across several UK institutions and programmes, including the University of Oxford's BOLD project, robotics safety research at Imperial College London and programmes at University College London.
Nvidia CEO Jensen Huang said AI capability and safety should advance together. The pledge demonstrates that investment in AI infrastructure can also support research into the safe development and evaluation of the systems that use it.
The announcement is notable because it shows that disagreements over regulation do not prevent investment in safety research. Companies can differ over whether governments should impose new legal requirements while still supporting technical work designed to identify risks.
Funding alone, however, cannot resolve the entire policy debate. Researchers also need appropriate access to models, independent evaluation methods and clear procedures for sharing findings that could improve safety across the industry.
Governments Are Taking Different Approaches to AI Risks
National governments face a different set of pressures from technology companies. They must consider public safety, economic competitiveness, national security and the potential effects of AI on employment and critical infrastructure.
In the United States, the federal government's June 2026 executive order on advanced AI emphasized innovation, security and cooperation with industry. It directed agencies to develop a voluntary framework for certain frontier models and explicitly ruled out creating a mandatory government licensing or preclearance requirement under that order.
This approach reflects a preference for accelerating AI development while coordinating with companies on security. It differs from proposals that would require stronger legal oversight before particularly capable systems are released.
The European Union has pursued a regulatory framework that places obligations on AI providers according to the relevant legal requirements and risk categories. Its approach reflects a broader emphasis on demonstrating compliance and protecting people affected by AI systems.
The UK is continuing to develop its position, including through its AI Security Institute and international cooperation on evaluation methods. The country is also facing growing pressure to clarify whether voluntary arrangements are sufficient for the most capable systems.
China's approach is shaped by its own technology policies, national security priorities and competition with the United States. Chinese officials and state-backed commentary have raised concerns about the strategic implications of AI restrictions, while also discussing security risks posed by advanced models.
These differences make international coordination difficult. A rule accepted by one government may be seen by another as an obstacle to economic development or a potential source of strategic disadvantage.
Why International Cooperation Matters
AI systems can be developed in one country, hosted in another and used by people around the world. A major security weakness in a widely available model can therefore have consequences that cross national borders.
International cooperation could help governments and researchers develop common methods for testing advanced models, reporting serious vulnerabilities and assessing whether safeguards are working. Shared standards could also reduce the burden on companies that operate across multiple jurisdictions.
In September 2026, the Dutch government published a joint international statement calling for stronger control of frontier AI models. The statement highlighted concerns about systems circumventing testing safeguards, exploiting vulnerabilities and gaining unauthorized access to real-world systems.
It also stressed that AI oversight should not widen the gap between countries in their ability to access the technology's benefits.
That concern is particularly relevant to developing economies. Countries with limited computing infrastructure, technical expertise or regulatory resources may struggle to evaluate advanced systems independently. At the same time, they may benefit considerably from AI applications in education, agriculture, healthcare and public services.
International cooperation will not automatically eliminate disagreements. Governments still have different economic priorities, security concerns and political systems. But shared testing methods and clearer expectations could make it easier to identify risks without requiring every country to adopt identical laws.
What AI Safety Means for Ordinary Users and Businesses
Although discussions about existential risk can sound distant, AI safety already affects everyday decisions.
A business using AI to process customer information needs to consider data protection, accuracy and access controls. A developer connecting an AI agent to business software must think about what actions the system can perform and whether a mistake could expose sensitive information or disrupt operations.
Users also need to understand that AI-generated answers can be incorrect, incomplete or misleading. A confident response is not proof that the information is accurate, and important decisions should not depend on unverified AI output alone.
For businesses, effective safeguards can include limiting system permissions, reviewing high-impact actions, testing applications before deployment and maintaining human oversight where errors could have serious consequences. The exact measures depend on the application and the level of risk.
These practical concerns differ from hypothetical scenarios involving future superintelligent systems, but they belong to the same wider discussion about how much autonomy AI should receive and how responsibility should be assigned when something goes wrong.
Clearer standards could help companies understand their obligations and give customers greater confidence in AI-powered products. Poorly designed rules, on the other hand, could impose costs without necessarily improving safety.
The Central Question: How Much Control Is Enough?
The disagreement over AI doom fears is unlikely to disappear soon because it involves both technical uncertainty and competing policy priorities.
Some of the most serious concerns relate to systems that may become more capable in the future. Predicting their behaviour is difficult, and experts disagree about the likelihood and timing of extreme outcomes. That uncertainty makes it challenging to decide when preventive restrictions are justified.
Waiting for complete certainty could leave governments unprepared for risks that emerge quickly. Acting on every worst-case scenario, however, could impose costly restrictions based on assumptions that later prove inaccurate.
A practical approach would distinguish between demonstrated risks and more speculative possibilities, while ensuring that serious emerging threats receive appropriate attention. It would also combine technical evaluations with accountability, independent oversight where justified and cooperation between governments and AI developers.
For technology companies, the challenge is to demonstrate that safety measures are more than public commitments. For governments, it is to establish clear expectations and credible oversight without unnecessarily blocking beneficial research and applications.
The debate is no longer simply about whether AI will transform society. That transformation is already underway. The more immediate question is whether the institutions responsible for developing and governing AI can adapt quickly enough to manage its risks while preserving its potential benefits.
Sources
- Reuters, “Factbox-Tech leaders, governments split over ‘AI doom’ fears” — https://www.investing.com/news/stock-market-news/factboxtech-leaders-governments-split-over-ai-doom-fears-4908878
- Reuters, “Nvidia pledges $250 million to UK AI safety research” — https://www.reuters.com/technology/nvidia-pledges-250-million-boost-uk-ai-safety-research-2026-10-14/
- WIRED, “OpenAI and Anthropic Tell British Lawmakers: Regulate Us” — https://www.wired.com/story/openai-and-anthropic-tell-british-lawmakers-regulate-us
- Government of the Netherlands, “A Call for Control of Frontier AI Models” — https://www.government.nl/documents/2026/09/22/a-call-for-control-of-frontier-ai-models
- The White House, “Promoting Advanced Artificial Intelligence Innovation and Security” — https://www.whitehouse.gov/presidential-actions/2026/06/promoting-advanced-artificial-intelligence-innovation-and-security/
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0