











































Bitcoin Miners Hijacked Through Luxor Software as Rewards Flowed to an Attacker's Wallet
Attackers broke into Luxor's Commander fleet-management software on November 15 and redirected thousands of customers' Bitcoin miners to the OCEAN pool, sending the rewards to a wallet they controlled. Luxor patched the flaw within two hours and says it will pay every affected customer in full, but the pool's payout rules meant the attacker's address kept receiving payments even after the hijack was stopped.
Bitcoin Miners Hijacked Through Luxor Software as Rewards Flowed to an Attacker's Wallet
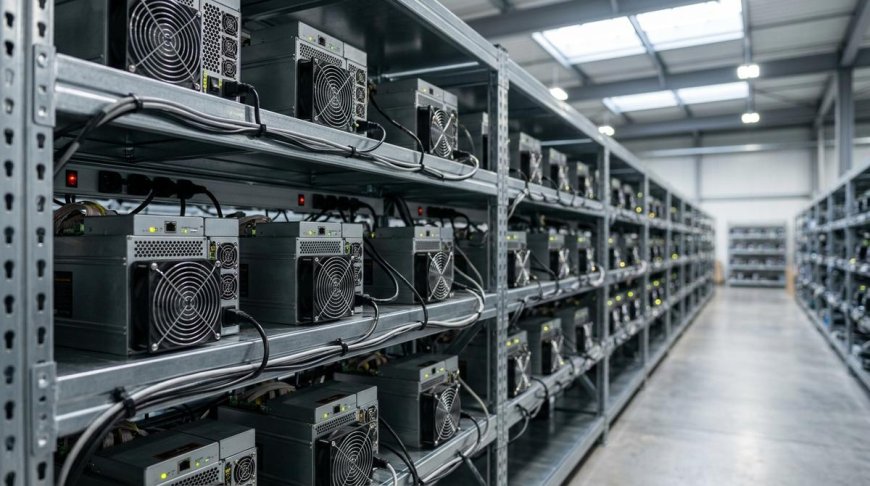
Thousands of Bitcoin mining machines spent part of their weekend working for someone else. Attackers broke into the fleet-management software of mining-services provider Luxor and quietly redirected customers' machines to a different mining pool, sending the Bitcoin those machines earned to a wallet controlled by the attackers — while the machines' real owners kept paying the electricity bills.
Luxor confirmed the breach on Sunday, November 15, and says it patched the flaw within two hours. The company has promised to pay every affected customer in full, as if their machines had mined normally. But the incident has already become a case study in how a single piece of management software can turn into a lever for redirecting an industrial-scale slice of the Bitcoin network — and how a mining pool's own payout rules can keep paying an attacker after the attack is over.
How the hijack unfolded
The target was Commander, Luxor's fleet-management platform, which lets mining operators monitor large numbers of machines and change their settings remotely from a single dashboard. Attackers used their access to Commander to change the pool and payout settings on machines belonging to just over a dozen customer accounts, pointing them at OCEAN, a separate Bitcoin mining pool, and at a Bitcoin address the attackers controlled.
Mining hosting firm CoreX Hosting raised the alarm first, after it noticed client machines connecting to OCEAN when they were configured for other pools. CoreX estimated that about 64,000 machines were affected, representing roughly 13 exahashes per second of computing power — around 1.4 percent of the entire Bitcoin network's hashrate at the time. Those figures are CoreX's estimates; Luxor's own statement did not repeat the machine count or the hashrate figure, and confirmed only that just over a dozen client accounts were involved.
The intrusion began in the early hours of Sunday, November 15 — reports put the start at around 6 p.m. Pacific time on Saturday, November 14. CoreX was still reporting the attack as ongoing roughly two hours later, with the attacker's address sitting at about 13 EH/s. Luxor says its engineers patched Commander within two hours of the breach being detected and then began restoring the affected machines to their original pool settings.
The payouts kept coming after the attack stopped
Changing a miner's pool and payout settings does not take the machine offline. It simply assigns the machine's earnings to someone else. That is why the first reports that the attacker had earned nothing turned out to be premature.
OCEAN pays miners for the work they submitted recently whenever the pool finds a block, even if those miners have since disconnected. Under the pool's rolling reward window, previously submitted shares stay eligible for a share of later block rewards. The hijacked machines never found a block themselves, but the work they did while redirected still counted.
The result: the address flagged by CoreX has received three block-reward payments totalling about 0.243 BTC, worth roughly $15,700, according to blockchain records reviewed by CoinDesk. None of the funds had been spent as of Monday morning. Earlier reports had counted two payments worth about 0.162 BTC, or roughly $10,500; a third payment arrived later.
More payments may still follow. Former OCEAN co-founder Luke Dashjr has claimed the pool could send the attacker's address roughly another $21,400 over the following day, and that OCEAN would keep nearly $650 in fees from the incident. Those figures are Dashjr's claims, not confirmed payments, and the payouts stop once the attacker's shares fall out of OCEAN's reward window.
OCEAN's design makes it a convenient destination for this kind of scheme. Miners connect to the pool using a Bitcoin address as their username, with no account and no identity check, and the pool pays rewards directly to that address inside the block's coinbase transaction — the first transaction in each block, which creates the newly issued coins.
Luxor's response
In a statement published on X on November 15, Luxor said no data was leaked or taken from its systems, and that its own mining pool and its LuxOS firmware were not affected. The company said Commander was patched within two hours, that restoration of affected machines to their original pool settings was under way, and that every affected client would be paid in full for the redirected hashrate.
Luxor chief executive Nick Hansen described the intrusion as using a "sophisticated AI-enabled vector" in a post on X on Monday, without explaining how artificial intelligence was used or how the attackers gained access. In a separate post, Hansen said Luxor had put most new feature development on hold while responding to weeks of AI-assisted attacks, with engineers rotating access keys, updating systems and addressing newly disclosed vulnerabilities.
AI has increasingly surfaced around Bitcoin security incidents in recent months, though evidence that attackers themselves used it has often been incomplete. In July, attackers exploited weak randomness in older Coldcard firmware to drain as much as $114 million from more than 5,000 addresses; Coldcard maker Coinkite later said it believed powerful AI models may have helped find the five-year-old flaw. In August, attackers exploited BTCPay Server software to steal credentials controlling merchant Lightning nodes and drain their funds; the flaw had been surfaced in an AI-assisted security review, while BTCPay said AI may also have helped attackers exploit it.
Why it matters
The Luxor incident shows where the real attack surface in industrial Bitcoin mining now sits. It is not the machines themselves, and it is not the Bitcoin blockchain — it is the control plane: the fleet-management software that decides, for tens of thousands of machines at once, which pool they work for and who gets paid.
A single compromised dashboard was enough to move an estimated 1.4 percent of the network's computing power. The machines kept running, the owners kept paying for power, and the rewards flowed elsewhere — and because of how the destination pool pays out, the money kept arriving after the hijack had been stopped.
For mining operators, the lesson is blunt: whoever controls the software that points the machines controls the revenue. For the rest of the industry, the open question is the one Luxor has not yet answered — a full post-mortem explaining how the attackers got in, and whether the "AI-enabled" label describes a genuinely new kind of attack or a familiar intrusion dressed up for a new era. Luxor says a full post-mortem is coming.
Sources
- CoinDesk — Bitcoin miners were hijacked and their rewards redirected to an attacker (November 16, 2026)
- CryptoSpiel — Luxor Hack Sent Clients' Bitcoin Miners to Work for a Thief
- Blockchain Reporter — Luxor Commander Hijack: 0.162 BTC in Payouts
- TradingView / Crypto Briefing — Luxor CEO warns of rising AI-enabled cyberattacks after mining hijack
- TradingView / BeInCrypto — How Did a Bitcoin Miner Hacker Get Paid Without Finding a Single Block?
Related reading on Innopark IT: Binance closes the $6.34 billion gap from its record October hack and Notion AI chat transcripts exposed in the Fireworks AI breach.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0